
Data Privacy & Compliance
Shein’s Android app breached clipboard privacy.
According to a blog post by Microsoft Threat Intelligence, the Shein shopping platform app owned by a Chinese company was found to be accessing user clipboards on Android devices.…
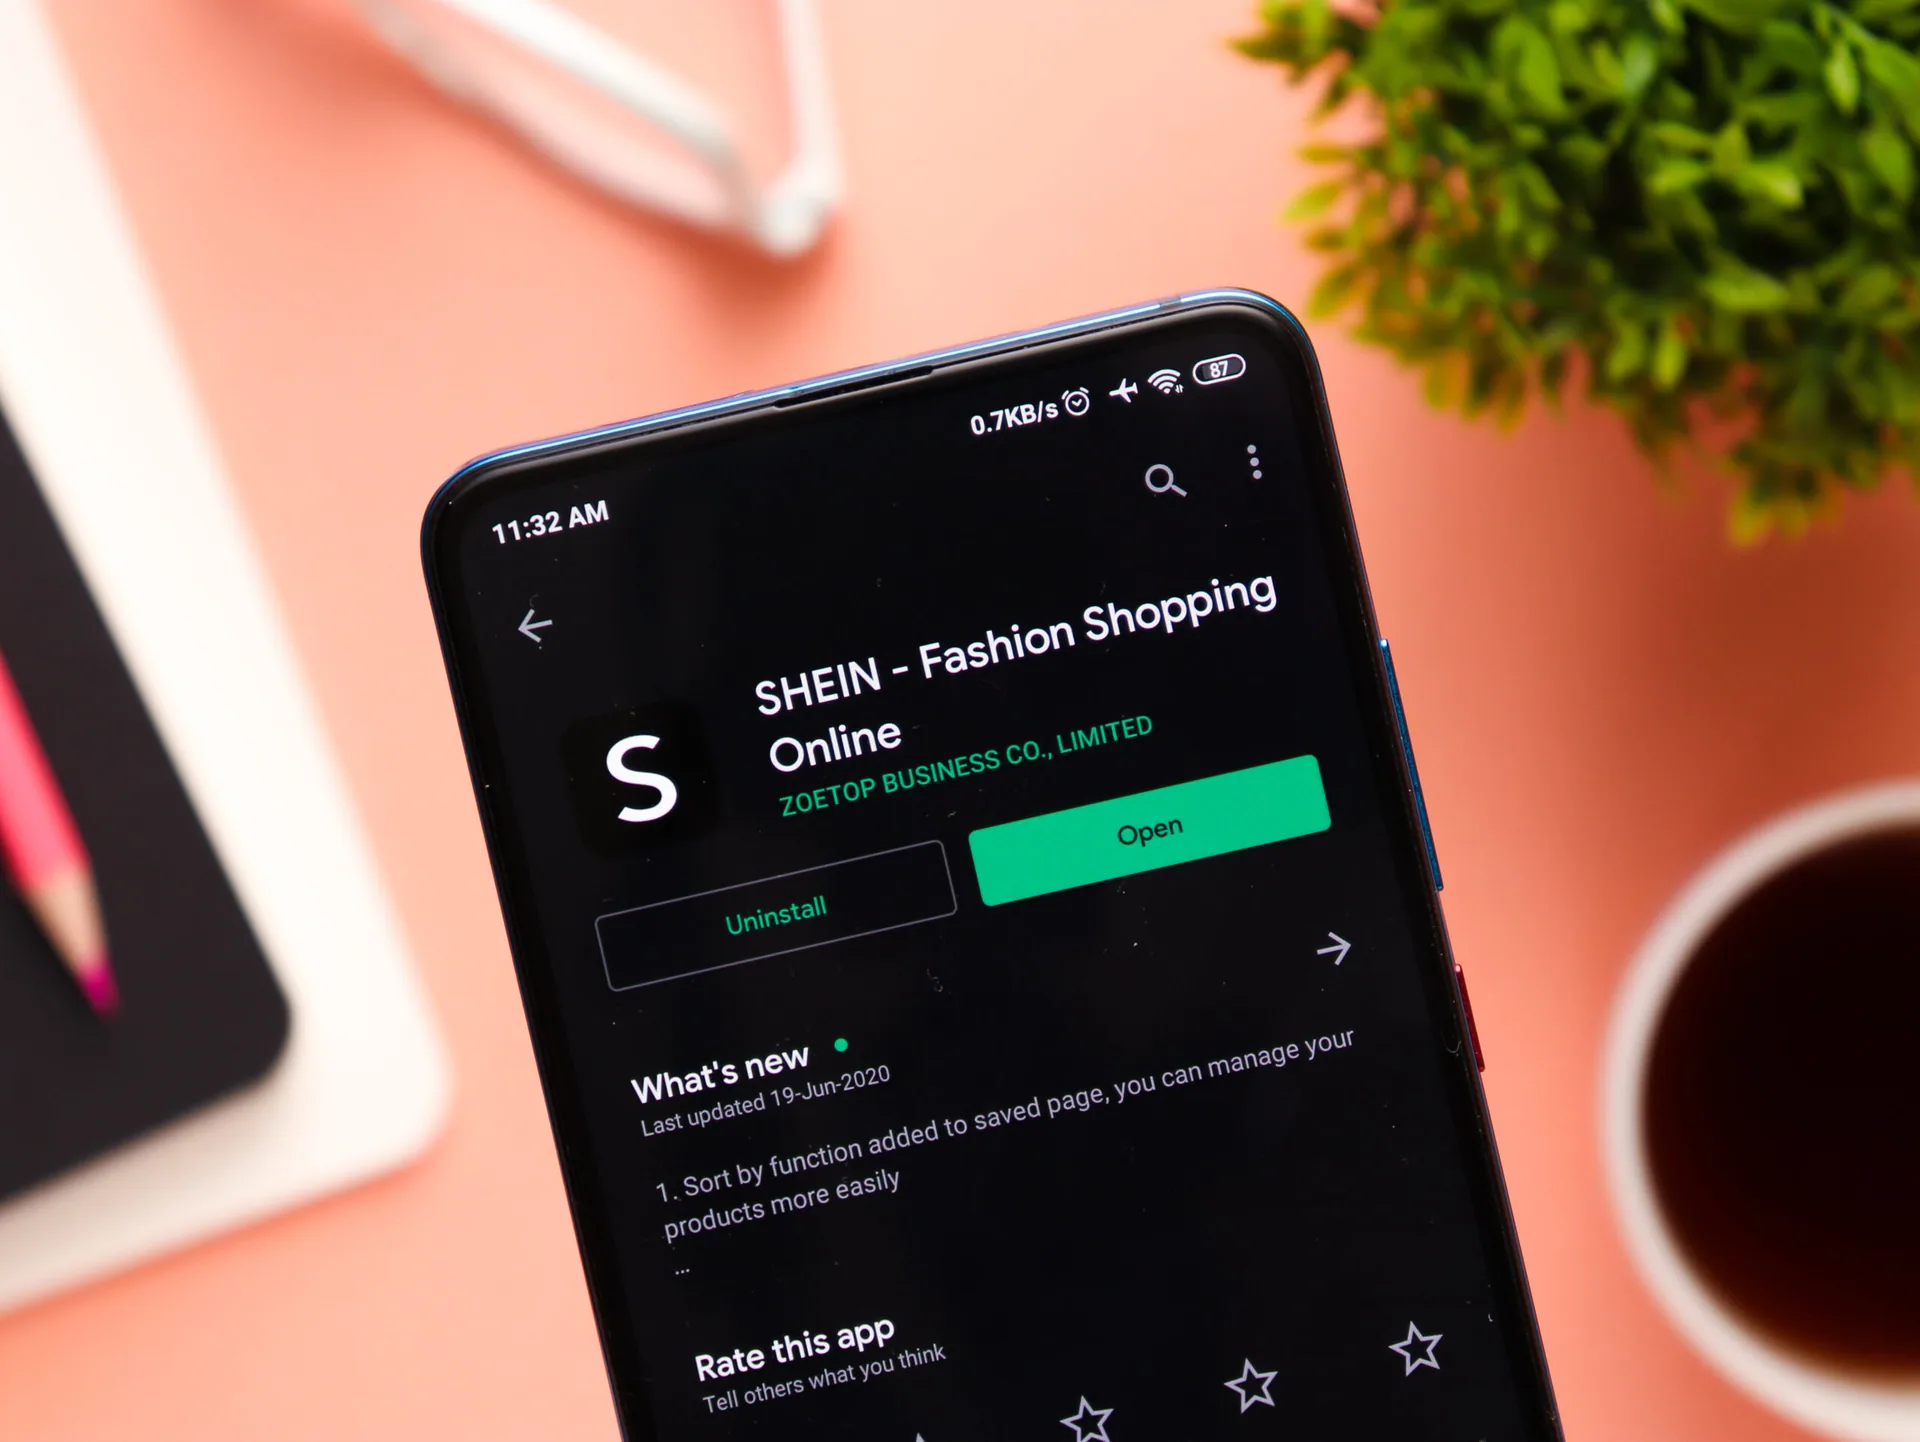
According to a blog post by Microsoft Threat Intelligence, the Shein shopping platform app owned by a Chinese company was found to be accessing user clipboards on Android devices.
“Microsoft discovered that an old version of the SHEIN Android application periodically read the contents of the Android device clipboard and, if a particular pattern was present, sent the contents of the clipboard to a remote server. While we are not specifically aware of any malicious intent behind the behavior, we assessed that this behavior was not necessary for users to perform their tasks on the app.” Said the Microsoft blog post.
As mentioned the issue is no fixed “We reported our findings to Google, the Play Store operator, leading to an investigation by their Android Security Team. In May 2022, Google informed us and we confirmed that SHEIN removed the behavior from the application. We would like to thank Google’s Android Security Team as well as the SHEIN team for their efforts and collaboration in addressing this issue. “
However, users must update their apps to avoid any potential danger. Device clipboards can contain sensitive data such as passwords, account numbers, and auto-fill information, making this behavior a potential security threat.
To protect against this and similar security risks, we advise users to follow the below security guidelines:
- Keep both the device and installed applications up-to-date.
- Avoid installing applications from untrusted sources.
- If an application exhibits unexpected behavior, such as displaying toast notifications with clipboard access, consider uninstalling it and reporting the behavior to the vendor or app store operator.
Source
- https://thehackernews.com/2023/03/sheins-android-app-caught-transmitting.html
- https://www.microsoft.com/en-us/security/blog/2023/03/06/protecting-android-clipboard-content-from-unintended-exposure/
Recently,
LastPass breach caused by engineer’s outdated Plex software.
Related articles
All insights
Sri Lanka’s PDPA Countdown Has Begun: Compliance Priorities for Businesses
Introduction After years of delays, Sri Lanka’s Personal Data Protection Act (PDPA) has finally reached a major milestone. The Government has confirmed that key operational…

PDPA in Sri Lanka: What Businesses Still Get Wrong
You can’t secure what you don’t truly understand. When the Personal Data Protection Act No. 9 of 2022 (PDPA) was introduced, it marked a turning point in how organizations across…
DLP: The Core of Modern Cybersecurity
In 2025, organizations operate in a world where data moves freely, quickly, and often invisibly across cloud platforms, mobile devices, SaaS tools, and third-party environments.…