Cyber resilience starts before the incident.Explore our security assessment services
Cyber Labs

Security Assessments

Security Hardening

Cyber Labs offers Security Hardening services to strengthen the resilience of systems, applications, and infrastructure against evolving threats. This service ensures that your environment is configured securely, aligned with industry benchmarks, and capable of withstanding real-world attack scenarios.

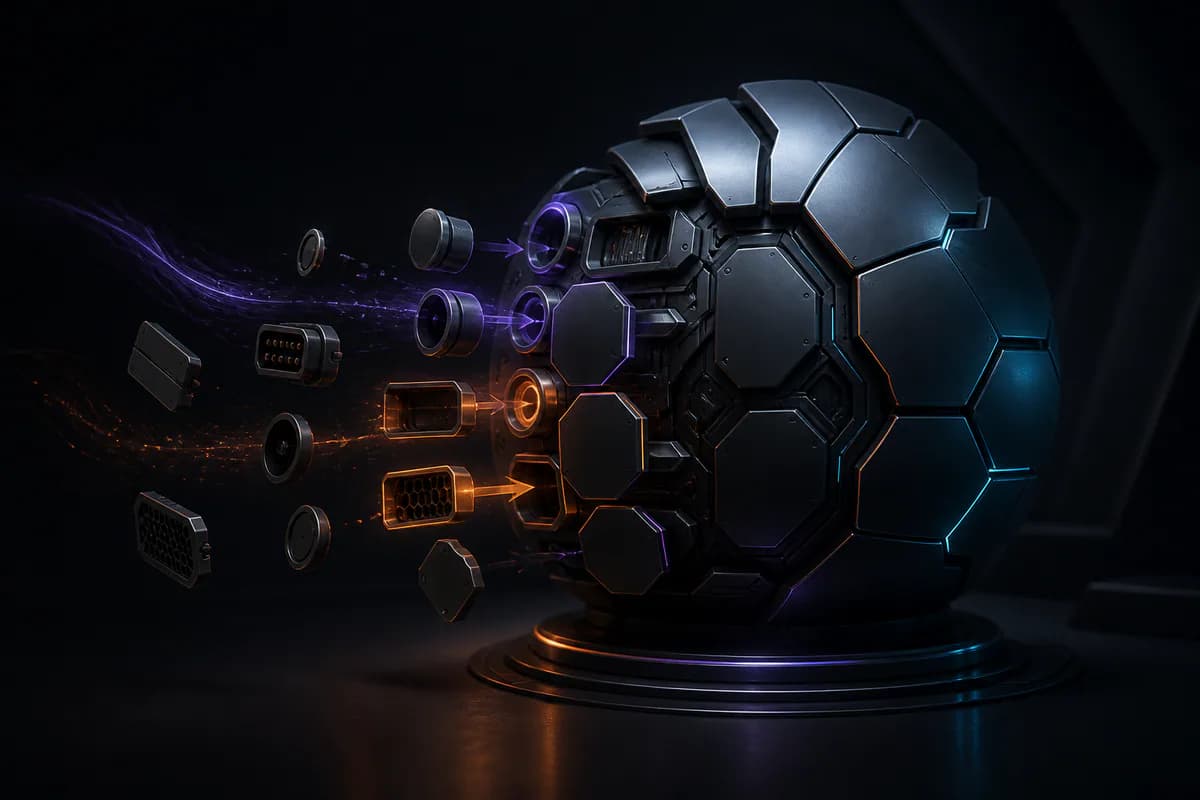
A system core gains fitted armour as unnecessary ports and exposed components are removed

What it is

A targeted engagement that reviews and reinforces the configuration of operating systems, applications, databases, and network components. Cyber Labs applies hardening techniques based on CIS Benchmarks, vendor best practices, and regulatory frameworks tailored to your business context and threat profile.

Why it matters

Default configurations often leave systems exposed. Security hardening reduces attack surface, enforces least privilege, and ensures that only necessary services and ports are active. Cyber Labs helps organizations move from reactive patching to proactive defense.

Business outcomes

How this service helps your business

Reduced Attack Surface

Disable unnecessary services, ports, and protocols to minimize exposure.

Compliance Alignment

Ensure configurations meet ISO 27001, PDPA, CBSL, and other regulatory standards.

Operational Stability

Hardened systems are less prone to compromise, misconfiguration, and performance degradation.

Audit & Certification Readiness

Support internal audits and external assessments with documented hardening controls.

Tailored to Environment

Cyber Labs adapts hardening profiles to suit your infrastructure, business needs, and risk appetite.

Our approach

How we deliver

We follow a structured, proven methodology to ensure testing is thorough, repeatable, and business-focused. Each engagement is designed to deliver both technical depth and practical outcomes your teams can act on.

  1. Review current configurations across servers, endpoints, applications, and cloud environments.

  2. Align with CIS Benchmarks, vendor guidelines, and internal policies to define secure baselines.

  3. Apply configuration changes, enforce access controls, and implement secure defaults.

  4. Verify hardened states, document changes, and provide rollback plans where necessary.

  5. Recommend monitoring strategies, update cycles, and future-proofing techniques.

  6. Strengthen systems, applications, and infrastructure against evolving threats. Cyber Labs enforces secure configurations, reduces attack surfaces, and enhances overall resilience.

Next step

Talk to us about security hardening.

We will walk through scope, timing and what the engagement would actually involve — no obligation.