Cyber resilience starts before the incident.Explore our security assessment services
Cyber Labs

Consulting (Governance & Risk)

GDPR Implementation

Cyber Labs provides end-to-end consultancy to help organizations implement and operationalize GDPR compliance. Our service ensures that personal data is handled lawfully, transparently, and securely meeting both regulatory obligations and customer expectations.

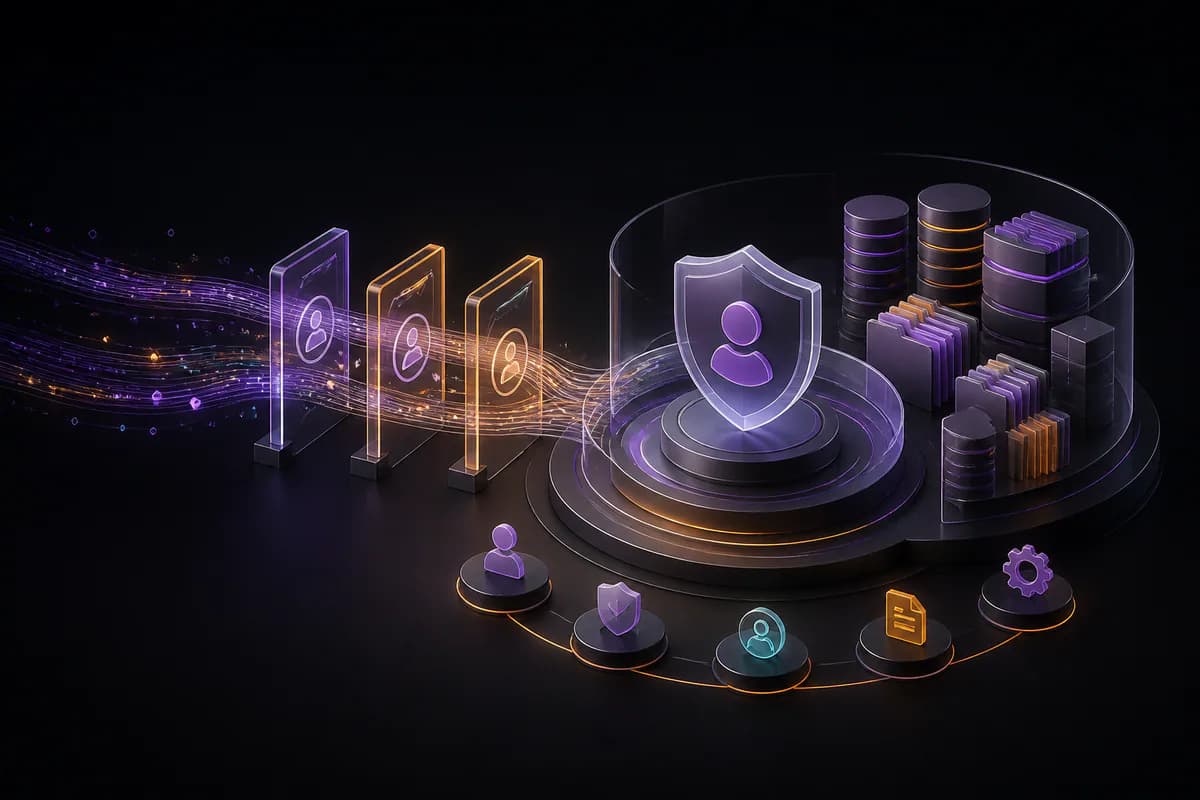
Personal information moves through transparent consent gates into a protected data environment

What it is

A structured consultancy engagement that supports the design, implementation, and governance of GDPR-aligned privacy programs. Cyber Labs helps organizations build data protection frameworks that are practical, scalable, and audit ready.

Why it matters

GDPR is more than a legal requirement. It’s a trust signal. Cyber Labs enables organizations to manage personal data responsibly, reduce regulatory risk, and strengthen customer confidence in how data is handled.

Business outcomes

How this service helps your business

Regulatory Compliance

Cyber Labs ensures alignment with GDPR principles, reducing exposure to fines and legal liabilities.

Customer Trust & Transparency

Clear data handling practices build credibility and strengthen relationships with clients and users.

Improved Data Governance

We help define ownership, access controls, and lifecycle management for personal data across systems.

Risk Reduction & Breach Preparedness

Cyber Labs implements controls that minimize the likelihood and impact of data breaches.

Audit & Documentation Readiness

We prepare organizations for regulatory audits with structured documentation, RoPA, DPIAs, and privacy policies.

Our approach

How we deliver

We follow a structured, proven methodology to ensure testing is thorough, repeatable, and business-focused. Each engagement is designed to deliver both technical depth and practical outcomes your teams can act on.

  1. Evaluate current data protection practices against GDPR requirements to identify gaps and risks.

  2. Identify personal data across systems, classify it by sensitivity, and map processing activities.

  3. Develop privacy policies, consent mechanisms, breach notification procedures, and data subject rights workflows.

  4. Establish roles such as DPO, define responsibilities, and set up internal reporting structures.

  5. Deliver tailored training for staff, contractors, and third parties to ensure GDPR awareness and accountability.

  6. Support internal audits, maintain RoPA and DPIAs, and refine controls based on evolving regulatory guidance.

  7. Build trust through privacy. Cyber Labs guides organizations to operationalize GDPR compliance, ensuring lawful, transparent, and secure handling of personal data.

Next step

Talk to us about gdpr implementation.

We will walk through scope, timing and what the engagement would actually involve — no obligation.