Cyber resilience starts before the incident.Explore our security assessment services
Cyber Labs

Security Assessments

API Security Assessment

Cyber Labs delivers targeted API Security Assessments to identify vulnerabilities, validate risks, and support remediation across web, mobile, and cloud-integrated APIs. Our approach combines automated scans, manual exploitation, and threat modeling aligned with OWASP API Top 10, MITRE ATT&CK.

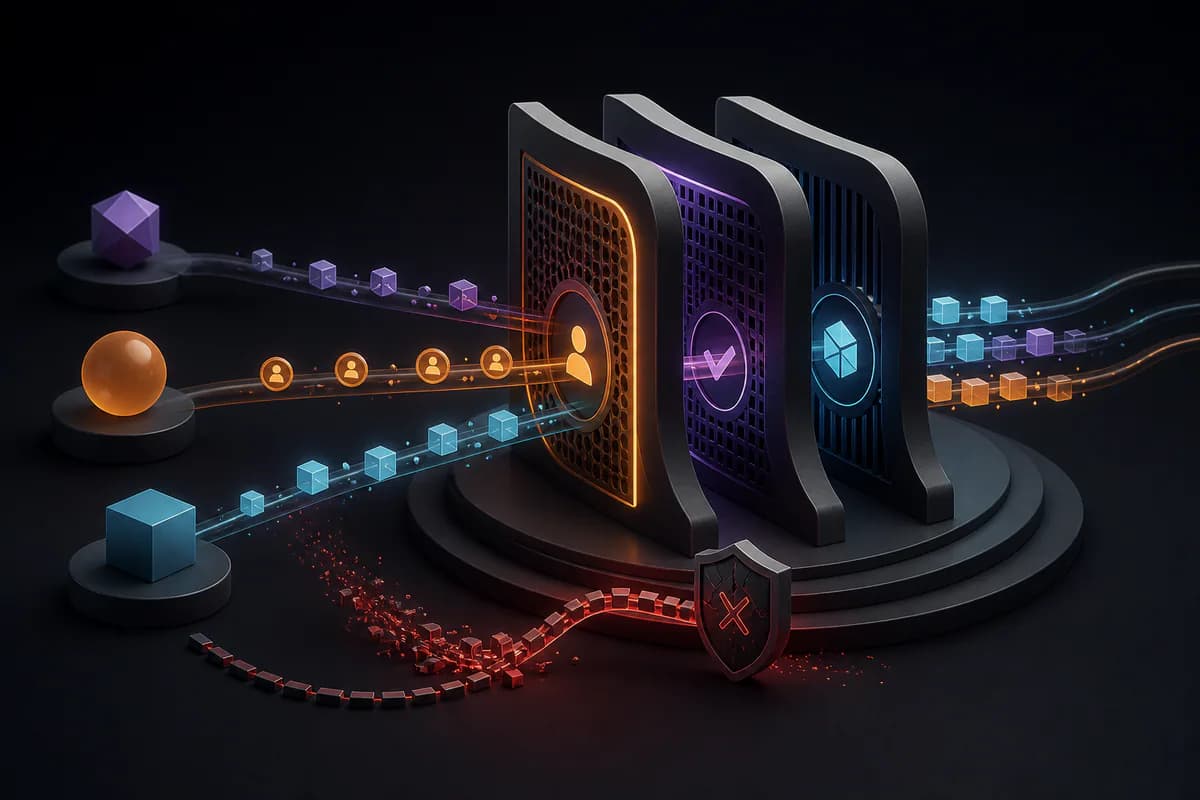
Identity tokens and data packets pass through protected API authorization gateways

What it is

A structured engagement that evaluates APIs for authentication flaws, data exposure, logic bypasses, and misconfigurations. Cyber Labs simulates real-world attack scenarios to uncover weaknesses in API endpoints, integrations, and backend services ensuring secure communication and access control.

Why it matters

APIs are the backbone of modern applications and a prime target for attackers. A single exposed endpoint can compromise entire systems. Cyber Labs helps organizations proactively secure APIs, protect sensitive data, and meet compliance requirements.

Business outcomes

How this service helps your business

Full-Stack API Coverage

We assess REST, SOAP, GraphQL, and mobile-integrated APIs covering authentication, authorization, and data handling.

Business Logic Validation

Cyber Labs identifies flaws in access control, rate limiting, and privilege escalation that automated tools often lack.

Threat-Aligned Testing

Our methodology maps to OWASP API Top 10 and MITRE ATT&CK techniques ensuring realistic threat simulation.

Actionable Reporting

We deliver executive summaries, technical findings, risk ratings, and remediation guidance with proof of concept and impact analysis.

Compliance & Audit Support

Testing aligns with ISO 27001, PCI DSS, PDPA, supporting regulatory and certification readiness.

Our approach

How we deliver

We follow a structured, proven methodology to ensure testing is thorough, repeatable, and business-focused. Each engagement is designed to deliver both technical depth and practical outcomes your teams can act on.

  1. Identify business-critical APIs, define threat vectors, and validate scope based on user roles and data flows.

  2. Run targeted scans using industry-standard tools to detect known vulnerabilities in endpoints and integrations.

  3. Validate findings through manual testing focusing on injection flaws, broken authentication, insecure deserialization, and logic bypasses.

  4. Deliver detailed reports with categorized findings, technical evidence, and tailored remediation recommendations. Support root cause analysis and future-proofing.

  5. Conduct rescans to confirm remediation effectiveness and ensure no new risks are introduced.

  6. Secure your APIs before attackers can exploit them. Cyber Labs identifies vulnerabilities, tests endpoints, and provides actionable guidance to protect your web, mobile, and cloud-integrated APIs.

Next step

Talk to us about api security assessment.

We will walk through scope, timing and what the engagement would actually involve — no obligation.