The Dark Side of SaaS: Hidden Security Risks in Cloud Applications
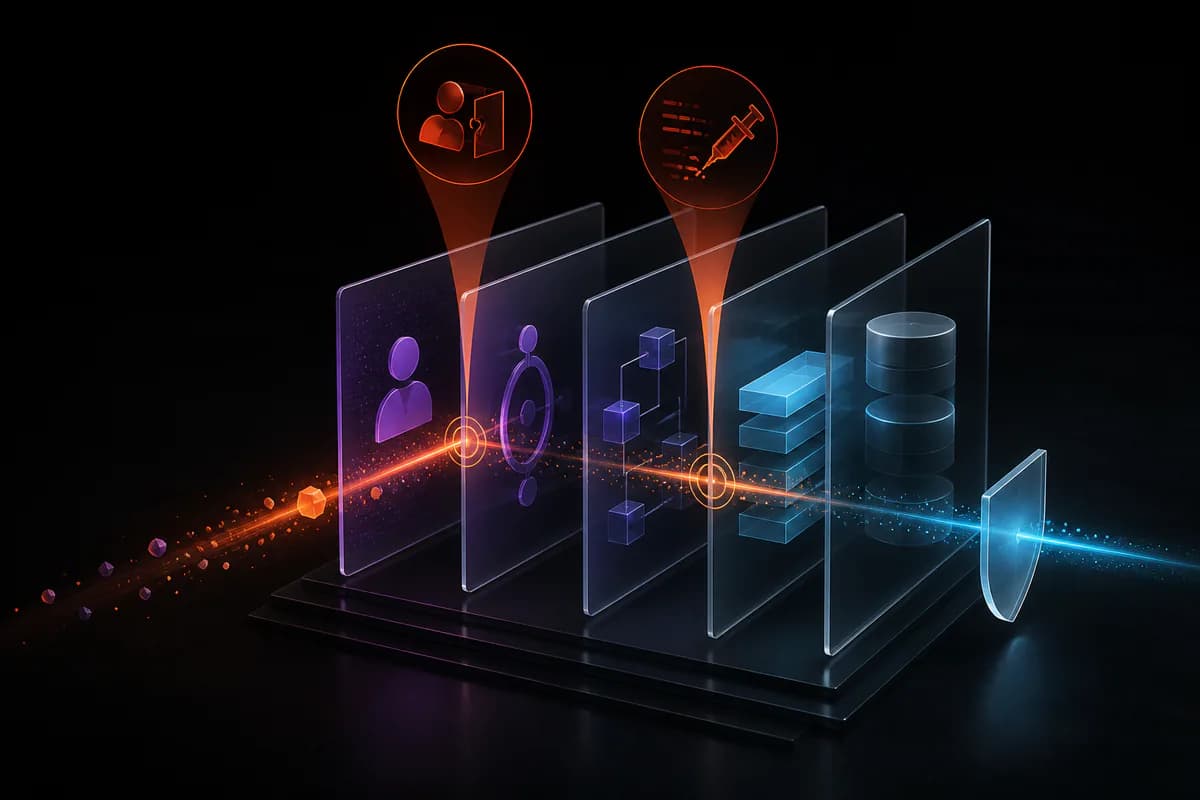
Organizations worldwide increasingly rely on Software as a Service (SaaS) application such as Google Workspace, Salesforce, Slack, and Microsoft 365 to streamline operations and…
Security Assessments
Cyber Labs delivers comprehensive Web Application Security Assessments to identify vulnerabilities, validate risks, and support remediation across web platforms. Our approach blends automated scanning with deep manual testing aligned to OWASP Top 10 and SANS Top 25 to ensure your applications are secure, resilient, and audit ready.

What it is
A structured engagement that evaluates web applications from both authenticated and unauthenticated perspectives. Cyber Labs simulates real-world attack scenarios to uncover flaws in logic, configuration, and code ensuring your application can withstand modern threats.
Why it matters
Web applications are prime targets for attackers. A single flaw can lead to data breaches, reputational damage, or regulatory penalties. Cyber Labs helps organizations proactively secure their digital assets, protect customer data, and maintain trust.
Business outcomes
We assess against OWASP Top 10, SANS Top 25, and custom business logic flaws ensuring full-spectrum visibility.
Cyber Labs emulates both external and internal threat actors using black box and gray box techniques.
Our reports include executive summaries, technical findings, risk ratings, and remediation guidance with evidence and impact analysis.
Testing aligns with ISO 27001, PCI DSS, GDPR, and PDPA, supporting regulatory and certification readiness.
We conduct rescans to verify remediation effectiveness and ensure no new risks are introduced.

Our approach
We follow a structured, proven methodology to ensure testing is thorough, repeatable, and business-focused. Each engagement is designed to deliver both technical depth and practical outcomes your teams can act on.
Understand the application’s structure, services, and interfaces from both unauthenticated and authenticated views. Define scope and impact zones.
Research and validate vulnerabilities manually and through automated tools prioritizing based on risk and exploitability.
Run in-depth scans using industry-standard tools to detect known vulnerabilities across the application stack.
Perform targeted manual exploitation to validate findings, assess impact, and uncover business logic flaws.
Deliver detailed reports with categorized findings, technical evidence, and tailored remediation recommendations. Support root cause analysis and future-proofing.
Protect your web applications from modern threats. Cyber Labs identifies vulnerabilities, tests logic and code, and provides actionable guidance to maintain secure, resilient, and audit-ready platforms.
Related services
Relevant insights

Organizations worldwide increasingly rely on Software as a Service (SaaS) application such as Google Workspace, Salesforce, Slack, and Microsoft 365 to streamline operations and…

Technical and infrastructure readiness is important for all organisations in terms of Cyber. How can you select your best vendor in the journey? With recent incidents observed…

In the modern era of technology, our workplaces lean heavily on digital tools, making us more vulnerable to cyber threats. However, we can effectively protect ourselves by…
Next step
We will walk through scope, timing and what the engagement would actually involve — no obligation.